Navigating the Healthcare Landscape: A Guide to HIPAA Compliance

Welcome to our HIPAA Compliance blog, your go-to resource for understanding, implementing, and maintaining compliance with the Health Insurance Portability and Accountability Act (HIPAA).

1. Introduction to HIPAA:
– Unveiling the purpose and significance of HIPAA in the healthcare industry.
– The impact on patient privacy, security, and data integrity.

2. HIPAA Privacy Rule:
– Exploring the privacy provisions of HIPAA.
– Patient rights, protected health information (PHI), and permissible uses.

3. HIPAA Security Rule:
– Understanding the security requirements for safeguarding electronic PHI (ePHI).
– Technical safeguards, physical safeguards, and administrative safeguards.

4. HIPAA Breach Notification Rule:
– Navigating the protocol for reporting and responding to data breaches.
– Requirements for timely notification and mitigation.

5. HIPAA Compliance for Healthcare Providers:
– Guidelines for healthcare professionals and organizations.
– Implementing policies and procedures to ensure compliance.

6. HIPAA Compliance for Business Associates:
– The responsibilities of third-party vendors and associates.
– Establishing secure partnerships to protect PHI.

7. Risk Assessments and Audits:
– Conducting thorough risk assessments to identify vulnerabilities.
– Strategies for internal and external audits to ensure ongoing compliance.

8. Training and Employee Awareness:
– Educating staff on HIPAA regulations and best practices.
– Fostering a culture of compliance within the healthcare organization.

9. Technology and HIPAA Compliance:
– Integrating secure technologies to protect ePHI.
– Encryption, access controls, and secure communication channels.

10. Ongoing Compliance Management:
– Establishing procedures for continuous monitoring and adaptation.
– Staying abreast of changes in HIPAA regulations and industry standards.

Embark on a journey with us as we delve into the intricacies of HIPAA Compliance. Whether you’re a healthcare professional, an IT specialist in the healthcare sector, or a business owner handling patient information, our content aims to empower you with the knowledge and tools necessary to ensure HIPAA compliance and the highest standards of data protection in the healthcare industry. Protect patient privacy, uphold HIPAA standards!

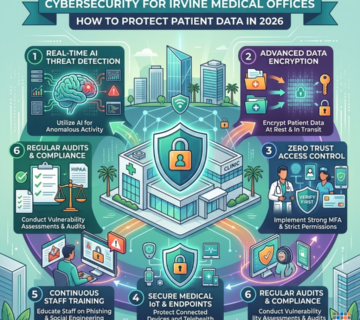
Cybersecurity for Irvine Medical Offices

Cybersecurity for Irvine Medical Offices: How to Protect Patient Data

Medical practices in Irvine are among the most targeted businesses for cyberattacks. Patient records sell for 10–50x the value of a credit card on the dark web, and most small clinics lack the IT security to defend against today's threats. The biggest risks facing Irvine healthcare offices in 2026 include ransomware, phishing emails, unsecured medical devices, insider threats, and cloud misconfigurations — any one of which can trigger a costly HIPAA breach. The average healthcare data breach now costs $10.9 million, and the Office for Civil Rights (OCR) is actively auditing small California practices. Under the HIPAA Security Rule, every medical office must have administrative, physical, and technical safeguards in place — covering everything from staff training and access controls to encryption and data backups. Penalties for non-compliance can reach $1.9 million per violation category. Technijian helps Irvine medical offices close these gaps fast with services including HIPAA Risk Assessments, 24/7 Managed Detection & Response, Penetration Testing, Security Awareness Training, and Microsoft 365 hardening — all built for healthcare environments in Orange County. ... Read More
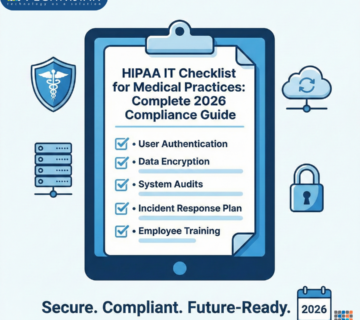
HIPAA Compliance Checklist Resources

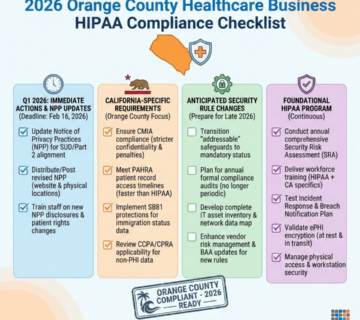
2026 HIPAA Compliance Checklist for Orange County Healthcare Businesses

As Orange County healthcare practices prepare for 2026, staying on top of HIPAA compliance is more critical than ever. This post provides a comprehensive checklist to help local healthcare organizations meet both federal and state requirements, covering everything from Privacy and Security Rules to Business Associate Agreements. It highlights common areas where practices often fall short, such as risk analysis, training records, and device encryption. Technijian, with years of expertise in healthcare IT, helps local organizations build and maintain robust compliance programs. If your practice hasn't reviewed its HIPAA program recently, this checklist is a crucial starting point. ... Read More
HIPAA Audits for Medical Device Firms

HIPAA Compliance for Medical Device Firms: Roles and IT Controls

When OCR sends a HIPAA audit notice to your Irvine medical device company, you have 60 days to prove compliance—or face penalties averaging $50,000. The critical mistake? Assuming clinical trial databases, quality complaint systems, and research participant records are protected with basic passwords and firewalls. Irvine's 400+ medical device manufacturers are discovering that unencrypted PHI, missing business associate agreements, and inadequate risk analyses trigger enforcement actions destroying hospital partnerships and delaying FDA submissions. Beyond penalties, violations cost lucrative contracts as healthcare systems now require vendor HIPAA compliance before procurement. The solution: specialized HIPAA compliant managed IT implementing encryption at rest, comprehensive audit logging, and OCR-ready documentation. Technijian delivers turnkey compliance for Orange County's medical technology sector since 2000. ... Read More