How to Prevent a Data Breach: Essential Tips for Businesses

Learn how to prevent a data breach with essential tips for businesses. Technijian offers strategies to safeguard your data and protect against cyber threats.

Security team in an Orange County office reviewing a data protection briefing on a wall screen

PwC Data Breach Claim: Everest Ransomware Group Says It Stole 590 GB of HR and Training Data

This Friday news brief examines the PwC data breach claim made by the Everest ransomware group, which says it holds 590 GB of human resources records, training materials, and single sign-on configuration files taken from a Cornerstone OnDemand staging environment. The claim is unverified and PwC has not responded. Written for business owners, operations leaders, and IT decision-makers throughout Orange County and Irvine, the brief explains what was alleged, why the reported record and file counts should not be read as confirmed numbers of affected people, and why a staging hostname changes the likely story. It sets out how to read any leak-site claim without over- or under-reacting, what HR and learning platforms expose to attackers, and a practical seven-step review of HR, learning, and test environments that organisations can complete this month before a listing ever names them. ... Read More
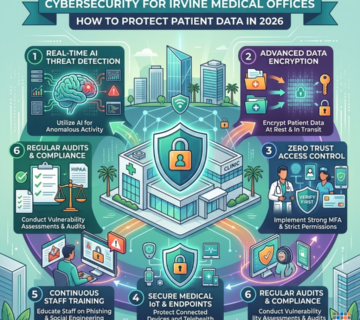
Cybersecurity for Irvine Medical Offices

Cybersecurity for Irvine Medical Offices: How to Protect Patient Data

Medical practices in Irvine are among the most targeted businesses for cyberattacks. Patient records sell for 10–50x the value of a credit card on the dark web, and most small clinics lack the IT security to defend against today's threats. The biggest risks facing Irvine healthcare offices in 2026 include ransomware, phishing emails, unsecured medical devices, insider threats, and cloud misconfigurations — any one of which can trigger a costly HIPAA breach. The average healthcare data breach now costs $10.9 million, and the Office for Civil Rights (OCR) is actively auditing small California practices. Under the HIPAA Security Rule, every medical office must have administrative, physical, and technical safeguards in place — covering everything from staff training and access controls to encryption and data backups. Penalties for non-compliance can reach $1.9 million per violation category. Technijian helps Irvine medical offices close these gaps fast with services including HIPAA Risk Assessments, 24/7 Managed Detection & Response, Penetration Testing, Security Awareness Training, and Microsoft 365 hardening — all built for healthcare environments in Orange County. ... Read More
Grubhub Data Breach

Grubhub Data Breach: What Customers Need to Know About the Recent Security Incident

This article examines the Grubhub data breach as a case study in modern supply chain cybersecurity vulnerabilities, where third-party platform compromises create cascading risks across interconnected business ecosystems. The incident demonstrates how attackers weaponize stolen OAuth tokens and access credentials from upstream service providers—specifically Salesforce and Zendesk integrations—to systematically infiltrate downstream customer systems without direct exploitation of primary infrastructure. Unlike traditional perimeter breaches that target individual organizations, this attack vector leverages the trust relationships inherent in SaaS-dependent architectures, enabling threat actors to access customer support data, contact records, and interaction histories across multiple corporate entities simultaneously. The breach highlights a fundamental shift in enterprise threat modeling, where vendor security posture becomes inseparable from organizational risk exposure. As food delivery platforms process millions of transactions containing personally identifiable information, delivery coordinates, and behavioral patterns, the incident underscores critical gaps in credential rotation protocols, token lifecycle management, and third-party security validation frameworks that define modern cloud-native vulnerability landscapes. ... Read More
Coupang Announces $1 17 Billion Compensation

Coupang Announces $1.17 Billion Compensation for Massive Data Breach Affecting 33.7 Million Customers

A historic $1.17 billion settlement by the e-commerce giant Coupang following a massive data breach that impacted over 33 million individuals. An internal employee allegedly orchestrated the cyberattack, which went undetected for several months before being linked to a former IT staff member. In response, the company has established a structured voucher system to compensate victims, including current and former customers, starting in early 2026. Beyond the immediate financial repercussions, the source emphasizes the critical importance of monitoring insider threats and maintaining robust detection systems to preserve consumer trust. It concludes by highlighting how proactive cybersecurity services can help organizations prevent similar large-scale vulnerabilities and navigate complex regulatory landscapes. ... Read More