Identity Security: Protecting Access in a Digital World

Identity security is the cornerstone of modern cybersecurity strategies, ensuring that only authorized individuals can access critical systems, data, and resources. As cyber threats grow increasingly sophisticated, protecting user identities has become more important than ever. Identity security involves multi-factor authentication, role-based access control, identity governance, and continuous monitoring to detect suspicious behavior. By securing identities, organizations prevent unauthorized access, data breaches, and insider threats. Strong identity security not only safeguards sensitive information but also builds trust with customers and partners. In an interconnected world, prioritizing identity protection is essential for maintaining operational resilience and regulatory compliance.

Secure Remote Access Policy Checklist planning for an Orange County business

My Security — Secure Remote Access Policy for Construction Companies
My Security — Secure Remote Access Policy for Construction Companies gives construction leaders and IT owners a practical framework for granting remote and jobsite access without exposing project data. This guide covers approved use cases, approved access methods, identity requirements, device conditions, vendor access control, data handling, logging and response, and testing and review. Orange County construction companies can use it to document current access paths, assign accountable owners, prioritize gaps, coordinate field crews, subcontractors and technology providers, and connect findings to a realistic access policy. It also explains the failure patterns to avoid and how to repeat the review after changes to systems, vendors, personnel, policies, risks, or project obligations. Use the policy as an operating process rather than a one-time exercise. ... Read More
Microsoft 365 Guest Access Review Checklist planning for an Orange County business

Microsoft 365 Guest Access Review for Healthcare Practices

Microsoft 365 Guest Access Review for Healthcare Practices gives healthcare leaders and IT owners a practical framework to control external access to Teams, SharePoint, OneDrive, and other shared resources. This guide covers guest inventory, accountable sponsorship, business associate relationships, current need, authentication, sharing restrictions, dormant accounts, exceptions, evidence, review triggers, offboarding, and implementation questions. Orange County healthcare organizations can use it to document current access, assign ownership, prioritize gaps, coordinate internal teams and vendors, and connect findings to a realistic Microsoft 365 security plan. It also explains how to validate completion and repeat reviews after changes to people, vendors, applications, policies, risks, or regulatory obligations. Use the checklist as an operating process rather than a one-time exercise. ... Read More
Privileged Access Review Checklist for Business Leaders planning for an Orange County business

Privileged Access Review Checklist for Business Leaders

Privileged Access Review Checklist for Business Leaders gives business, security, and technology leaders a practical framework to verify that administrative access remains necessary, controlled, monitored, and recoverable. This guide covers privileged-account inventory, ownership, current need, separate daily and administrative identities, authentication and recovery, third-party access, evidence, exceptions, review triggers, common failure patterns, and implementation questions. Orange County organizations can use it to document the current state, assign accountability, prioritize gaps, coordinate internal teams and providers, and connect findings to a realistic security plan. It also explains how to validate completion and repeat the review after material changes to people, systems, vendors, policies, risks, or business priorities. Use the checklist as an operating process rather than a one-time form. ... Read More
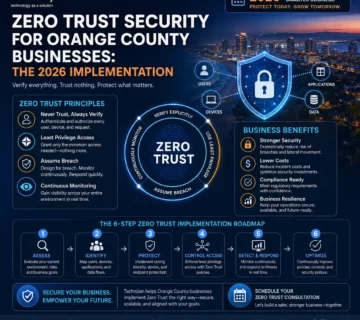
Zero Trust Security for Orange County Businesses: The 2026 Implementation

Zero Trust Security for Orange County Businesses: The 2026 Implementation Guide 

Zero Trust Security for Orange County Businesses is no longer optional in 2026. As traditional perimeter-based security fails in hybrid and cloud-driven environments, Zero Trust provides a modern approach based on “never trust, always verify.” This guide explains why legacy security models are ineffective, outlines the five pillars of Zero Trust architecture, and provides a practical implementation roadmap tailored for OC businesses. From identity verification and device compliance to microsegmentation and data protection, this blog helps organizations reduce breach risk, stop lateral movement, and secure critical systems in today’s evolving threat landscape. ... Read More
Major Australian Airline Faces Massive Customer Data Exposure: 5 7 Million Records Compromised

Major Australian Airline Faces Massive Customer Data Exposure: 5.7 Million Records Compromised

An Australian airline experienced a significant data breach in late June 2025, compromising 5.7 million customer records through a third-party service provider. The breach exposed various categories of personal information, including names, contact details, and loyalty program data, but critical security credentials like financial information remained secure. This incident is part of a broader trend of cybercrime syndicates targeting the aviation sector globally. The airline's corporate response includes transparent customer communication, offering guidance on personal security measures and collaborating with law enforcement. Technijian offers comprehensive cybersecurity solutions for both organizations and individuals, aiming to protect against similar sophisticated threats and enhance overall digital security. ... Read More