Secure Remote Access Policy Checklist planning for an Orange County business

My Security — Secure Remote Access Policy for Construction Companies
My Security — Secure Remote Access Policy for Construction Companies gives construction leaders and IT owners a practical framework for granting remote and jobsite access without exposing project data. This guide covers approved use cases, approved access methods, identity requirements, device conditions, vendor access control, data handling, logging and response, and testing and review. Orange County construction companies can use it to document current access paths, assign accountable owners, prioritize gaps, coordinate field crews, subcontractors and technology providers, and connect findings to a realistic access policy. It also explains the failure patterns to avoid and how to repeat the review after changes to systems, vendors, personnel, policies, risks, or project obligations. Use the policy as an operating process rather than a one-time exercise. ... Read More
Technology Vendor Exit Plan Checklist planning for an Orange County business

My IT — Technology Vendor Exit Plan for Hospitality Businesses

My IT — Technology Vendor Exit Plan for Hospitality Businesses gives hospitality leaders and IT owners a practical framework for leaving a technology vendor without losing data, access, or guest service. This guide covers contract and exit obligations, vendor-controlled asset inventory, organizational ownership, data export and validation, operational knowledge transfer, access revocation and replacement, successor coordination, and closing with evidence. Orange County hospitality businesses can use it to document current dependencies, assign accountable owners, prioritize gaps, coordinate property, front-desk and technology teams, and connect findings to a realistic transition plan. It also explains the failure patterns to avoid and how to repeat the review after changes to systems, vendors, personnel, policies, risks, or contractual obligations. Use the plan as an operating process rather than a one-time exercise. ... Read More
IT Change Management Checklist for Small Businesses planning for an Orange County business

My IT — Change Management Checklist for Retail and Ecommerce

My IT — Change Management Checklist for Retail and Ecommerce gives retail and ecommerce leaders and IT owners a practical framework for approving and releasing changes without disrupting trading. This guide covers change description, impact and risk assessment, approval authority, test planning, implementation and rollback steps, communication with affected people, outcome recording, and pattern review. Orange County retail and ecommerce businesses can use it to document current change practice, assign accountable owners, prioritize gaps, coordinate store, warehouse and technology teams, and connect findings to a realistic release calendar. It also explains the failure patterns to avoid and how to repeat the review after changes to systems, vendors, personnel, policies, risks, or peak-season obligations. Use the checklist as an operating process rather than a one-time exercise. ... Read More
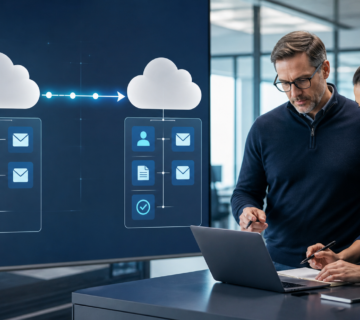
Technology specialists planning a tenant to tenant Microsoft 365 migration

My Office — Tenant-to-Tenant Microsoft 365 Migration for Professional Firms

My Office — Tenant-to-Tenant Microsoft 365 Migration for Professional Firms gives professional services leaders and IT owners a practical framework for moving a tenant without losing access, records, or client confidence. This guide covers business scope and decision authority, identity and access inventory, workload-by-workload scope, security, compliance and retention review, application dependency mapping, pilot validation, and cutover and stabilization planning. Orange County professional firms can use it to document the current tenant, assign accountable owners, prioritize gaps, coordinate internal teams and technology providers, and connect findings to a realistic migration plan. It also explains how to measure a pilot before committing and how to repeat the review after changes to systems, vendors, personnel, policies, or risks. Treat the framework as an operating process rather than a one-time project. ... Read More
Cyber Incident Communication Plan for Business Leaders planning for an Orange County business

My Security — Cyber Incident Communication Plan for Financial Firms

My Security — Cyber Incident Communication Plan for Financial Firms gives financial services leaders and IT owners a practical framework for deciding who speaks, to whom, and with what verified facts once an incident begins. This guide covers activation criteria, contact structure, audience and owner assignment, fact-validation rules, resilient communication channels, control of sensitive information, incident timelines, and post-incident review. Orange County financial firms can use it to document notification obligations, assign accountable owners, prioritize gaps, coordinate internal teams, counsel, and technology providers, and connect findings to a realistic incident response plan. It also explains the failure patterns to avoid and how to repeat the review after changes to systems, vendors, personnel, policies, risks, or client obligations. Use the plan as an operating process rather than a one-time document. ... Read More