Ransomware Attacks: Protect Your Business from Digital Extortion

Ransomware is a form of malicious software designed to encrypt a victim’s data until a ransom is paid. These attacks can cripple businesses, leading to data loss, financial damage, and reputational harm. To protect your business, implement robust cybersecurity measures like regular backups, employee training, and advanced threat detection systems. A proactive defense strategy is essential for mitigating the risks of ransomware and ensuring business continuity.

Incident response team isolating systems during the first 24 hours of a ransomware attack

How to Respond to a Ransomware Attack: The First 24 Hours

This comprehensive technical guide focuses on how to respond to a ransomware attack across small and mid-market organizations in Orange County, establishing documented containment procedures, verified incident oversight, and measurable recovery benchmarks delivered through My Security. Designed specifically for business owners, IT managers and operations leadership throughout Orange County and Irvine, this hour-by-hour framework helps isolate affected systems without destroying evidence, activate the right response team, notify legal counsel and cyber insurers on time, and verify backup integrity before restoring. We examine specific escalation triggers, evidence-preservation requirements, and practical decision procedures that prevent prolonged downtime and reduce regulatory liability. Organizations are encouraged to evaluate their current incident response posture against these benchmark standards and implement a tested, off-network checklist to ensure contained incidents, verified recovery, and continuous daily resilience. ... Read More
Security team in an Orange County office reviewing a data protection briefing on a wall screen

PwC Data Breach Claim: Everest Ransomware Group Says It Stole 590 GB of HR and Training Data

This Friday news brief examines the PwC data breach claim made by the Everest ransomware group, which says it holds 590 GB of human resources records, training materials, and single sign-on configuration files taken from a Cornerstone OnDemand staging environment. The claim is unverified and PwC has not responded. Written for business owners, operations leaders, and IT decision-makers throughout Orange County and Irvine, the brief explains what was alleged, why the reported record and file counts should not be read as confirmed numbers of affected people, and why a staging hostname changes the likely story. It sets out how to read any leak-site claim without over- or under-reacting, what HR and learning platforms expose to attackers, and a practical seven-step review of HR, learning, and test environments that organisations can complete this month before a listing ever names them. ... Read More
Ransomware Recovery Planning for Law Firms: What Partners Need Before an Incident featured image

Ransomware Recovery Planning for Law Firms: What Partners Need Before an Incident

Ransomware Recovery Planning for Law Firms: What Partners Need Before an Incident explains how law firms and security-conscious organizations can evaluate risk, improve safeguards, and protect sensitive business data in 2026. The article covers practical controls, common warning signs, documentation needs, and the operational decisions leaders should review before problems become expensive incidents. Readers will learn how to think about access, backups, vendor oversight, incident response, employee habits, and client expectations in a structured way. It is designed for partners, administrators, and business leaders who need plain-English cybersecurity guidance. Technijian can help review current gaps, prioritize security improvements, and implement practical protections that support compliance, continuity, and client trust. ... Read More
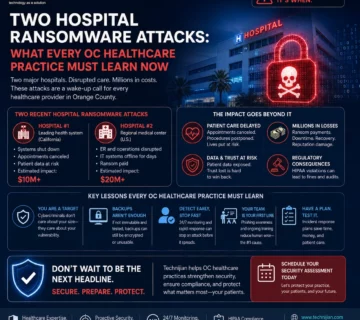
Two Hospital Ransomware Attacks: What Every OC Healthcare Practice Must Learn Now

Two Hospital Ransomware Attacks in 60 Days: What Every OC Healthcare Practice Must Learn Now 

In 2026, healthcare organizations across the U.S. faced severe ransomware attacks that disrupted patient care and exposed critical data. Practices in Orange County must understand the growing threat, which targets not only large hospitals but also small clinics and medical offices. This blog explores the latest ransomware trends, their impact on patient safety, and essential lessons for securing healthcare IT systems, including backup strategies, third-party vendor risks, and the importance of multi-factor authentication (MFA). With rising ransomware threats, every healthcare practice must act proactively to protect their operations and patient data. ... Read More
Tsundere Bot and the Evolution of TA584 Ransomware

Tsundere Bot Replaces Initial Access Hackers in Ransomware Attacks

Cybercriminal group TA584 has dramatically evolved its tactics, replacing traditional initial access hackers with advanced malware like Tsundere Bot. This sophisticated malware platform, part of a broader trend in the malware-as-a-service economy, allows attackers to bypass traditional defenses and execute fileless attacks. Tsundere Bot is enabling more efficient ransomware deployments, posing an increasing threat to businesses across multiple industries. Learn how this new wave of malware affects organizations and how to protect against such evolving threats in this comprehensive guide. ... Read More