

Incident response team isolating systems during the first 24 hours of a ransomware attack

How to Respond to a Ransomware Attack: The First 24 Hours

This comprehensive technical guide focuses on how to respond to a ransomware attack across small and mid-market organizations in Orange County, establishing documented containment procedures, verified incident oversight, and measurable recovery benchmarks delivered through My Security. Designed specifically for business owners, IT managers and operations leadership throughout Orange County and Irvine, this hour-by-hour framework helps isolate affected systems without destroying evidence, activate the right response team, notify legal counsel and cyber insurers on time, and verify backup integrity before restoring. We examine specific escalation triggers, evidence-preservation requirements, and practical decision procedures that prevent prolonged downtime and reduce regulatory liability. Organizations are encouraged to evaluate their current incident response posture against these benchmark standards and implement a tested, off-network checklist to ensure contained incidents, verified recovery, and continuous daily resilience. ... Read More
Technijian blog 53279 realistic workplace technology photo

Cyber Insurance Questionnaire Preparation and Security Controls

This comprehensive technical guide focuses on cyber insurance questionnaire help orange county across cross-industry mid-market organizations, establishing documented operational controls, verified technical oversight, and measurable service benchmarks delivered through My Compliance. Designed specifically for CFO / Controller / VP Finance leadership and corporate technology decision-makers throughout Orange County and Irvine, this operational framework helps resolve systemic workflow friction, eliminate administrative bottlenecks, reinforce data protection, and enforce resilient infrastructure standards across distributed environments. We examine specific assessment triggers, objective evidentiary requirements, and practical review procedures that prevent unplanned service downtime and reduce regulatory liability. Organizations are encouraged to evaluate their current operational posture against these benchmark standards and implement structured verification routines to ensure sustained compliance, verified audit readiness, and continuous daily resilience. ... Read More
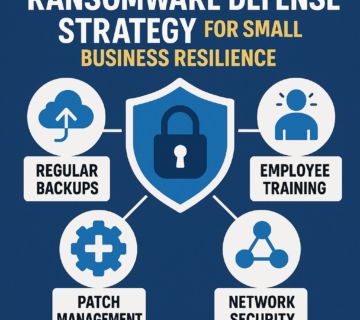
Cybersecurity for Small Businesses

Cybersecurity for Small Businesses: The 2025 Ransomware Defense Playbook

A comprehensive cybersecurity playbook detailing strategies for small businesses to defend against modern ransomware threats, which are characterized by costly, multi-stage attacks and the use of double-extortion tactics where data is stolen before encryption. The text outlines the need for a layered security architecture, recommending advanced technologies like Endpoint Detection and Response (EDR) and professional SOC monitoring to detect threats before widespread deployment occurs. Crucially, the guide underscores that recovery depends on utilizing the 3-2-1 backup rule along with immutable, air-gapped backups designed to survive attacks aimed at crippling restoration capabilities. Moreover, effective defense requires consistent employee security awareness training and the establishment of a robust, tested incident response plan to manage potential breaches and ensure regulatory compliance. Finally, the playbook suggests that smaller organizations should leverage managed security services, such as those offered by Technijian, to access enterprise-grade protection necessary to counteract sophisticated cybercriminal groups. ... Read More