Safeguard Your Business from Data Breaches

A data breach can have devastating consequences for any business, leading to financial losses, reputational damage, and legal complications. Protecting sensitive information is more critical than ever as cyberattacks become increasingly sophisticated. By implementing robust cybersecurity measures, such as encryption, multi-factor authentication, and regular security audits, businesses can significantly reduce the risk of a data breach. Stay vigilant and proactive to safeguard your company’s most valuable assets and maintain customer trust.

Security team in an Orange County office reviewing a data protection briefing on a wall screen

PwC Data Breach Claim: Everest Ransomware Group Says It Stole 590 GB of HR and Training Data

This Friday news brief examines the PwC data breach claim made by the Everest ransomware group, which says it holds 590 GB of human resources records, training materials, and single sign-on configuration files taken from a Cornerstone OnDemand staging environment. The claim is unverified and PwC has not responded. Written for business owners, operations leaders, and IT decision-makers throughout Orange County and Irvine, the brief explains what was alleged, why the reported record and file counts should not be read as confirmed numbers of affected people, and why a staging hostname changes the likely story. It sets out how to read any leak-site claim without over- or under-reacting, what HR and learning platforms expose to attackers, and a practical seven-step review of HR, learning, and test environments that organisations can complete this month before a listing ever names them. ... Read More
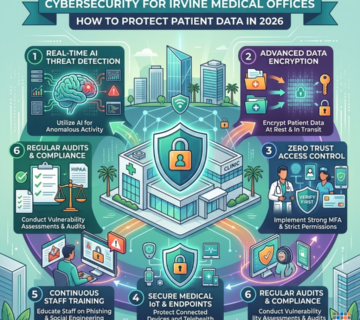
Cybersecurity for Irvine Medical Offices

Cybersecurity for Irvine Medical Offices: How to Protect Patient Data

Medical practices in Irvine are among the most targeted businesses for cyberattacks. Patient records sell for 10–50x the value of a credit card on the dark web, and most small clinics lack the IT security to defend against today's threats. The biggest risks facing Irvine healthcare offices in 2026 include ransomware, phishing emails, unsecured medical devices, insider threats, and cloud misconfigurations — any one of which can trigger a costly HIPAA breach. The average healthcare data breach now costs $10.9 million, and the Office for Civil Rights (OCR) is actively auditing small California practices. Under the HIPAA Security Rule, every medical office must have administrative, physical, and technical safeguards in place — covering everything from staff training and access controls to encryption and data backups. Penalties for non-compliance can reach $1.9 million per violation category. Technijian helps Irvine medical offices close these gaps fast with services including HIPAA Risk Assessments, 24/7 Managed Detection & Response, Penetration Testing, Security Awareness Training, and Microsoft 365 hardening — all built for healthcare environments in Orange County. ... Read More
ClickFix

New ClickFix Attack Targeting Windows and macOS Users to Deploy Infostealer Malware

ClickFix, a sophisticated social engineering attack active in 2025 that deploys infostealer malware against both Windows and macOS users. This technique is highly effective because it bypasses traditional security tools by manipulating users into executing malicious fileless commands disguised as legitimate troubleshooting steps, leveraging trusted platforms like Google services to maintain credibility. The text explains the distinct attack vectors for Windows (distributing ACR stealer via fake software archives) and macOS (using a fake Cloudflare prompt to execute the Odyssey stealer via the Terminal), emphasizing the challenges security solutions face with this memory-resident malware. Finally, the document concludes with advice on recognizing and avoiding ClickFix, along with a pitch from Technijian, an Orange County-based Managed IT Services provider, detailing their services for helping organizations defend against such advanced cross-platform social engineering attacks. ... Read More
Google Takes Legal Action

Google Takes Legal Action Against Chinese Phishing Network Targeting American Consumers

Google against a sophisticated Chinese phishing-as-a-service platform called "Lighthouse," which has facilitated text message scams (smishing) targeting over a million consumers globally, often by impersonating entities like the USPS and toll authorities. The operation, traced to a Chinese threat actor, offers subscription-based access to tools that lower the barrier to entry for cybercriminals and is alleged to have compromised millions of payment cards through convincing fraudulent websites that sometimes misuse Google's trademarks. In response, Google is enhancing its AI-powered security features and supporting legislative initiatives to combat international cybercrime. Additionally, the text includes a section from a company named Technijian, which markets its cybersecurity and managed IT services to businesses in Orange County, California, as a solution to defend against threats such as the Lighthouse platform. ... Read More