Data Protection

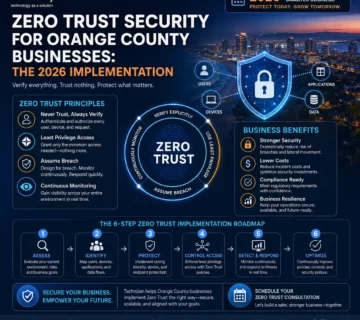
Zero Trust Security for Orange County Businesses: The 2026 Implementation

Zero Trust Security for Orange County Businesses: The 2026 Implementation Guide 
Zero Trust Security for Orange County Businesses is no longer optional in 2026. As traditional perimeter-based security fails in hybrid and cloud-driven environments, Zero Trust provides a modern approach based on “never trust, always verify.” This guide explains why legacy security models are ineffective, outlines the five pillars of Zero Trust architecture, and provides a practical implementation roadmap tailored for OC businesses. From identity verification and device compliance to microsegmentation and data protection, this blog helps organizations reduce breach risk, stop lateral movement, and secure critical systems in today’s evolving threat landscape. ... Read More
HIPAA Audits for Medical Device Firms

HIPAA Audits for Medical Device Firms in Irvine: HIPAA Compliant Managed IT Irvine CA 2026 

When OCR sends a HIPAA audit notice to your Irvine medical device company, you have 60 days to prove compliance—or face penalties averaging $50,000. The critical mistake? Assuming clinical trial databases, quality complaint systems, and research participant records are protected with basic passwords and firewalls. Irvine's 400+ medical device manufacturers are discovering that unencrypted PHI, missing business associate agreements, and inadequate risk analyses trigger enforcement actions destroying hospital partnerships and delaying FDA submissions. Beyond penalties, violations cost lucrative contracts as healthcare systems now require vendor HIPAA compliance before procurement. The solution: specialized HIPAA compliant managed IT implementing encryption at rest, comprehensive audit logging, and OCR-ready documentation. Technijian delivers turnkey compliance for Orange County's medical technology sector since 2000. ... Read More
How Technijian Can Help Your Law Firm Achieve SOC 2 Type 2 Compliance 

Why Your Law Firm Needs SOC 2 Type 2 Compliant IT for Law Firms Irvine 

SOC 2 Type 2 compliance has become essential for law firms handling sensitive client data in 2026. This certification demonstrates that your IT infrastructure maintains continuous security controls over time, protecting attorney-client privilege and meeting regulatory requirements. For law firms throughout Irvine, Newport Beach, Costa Mesa, Santa Ana, Anaheim, Tustin, Mission Viejo, Lake Forest, Huntington Beach, Fullerton, and all of Orange County, partnering with SOC 2 Type 2 compliant IT for law firms Irvine providers like Technijian ensures your firm meets the rigorous standards corporate clients and auditors now demand. This guide explains what SOC 2 Type 2 certification means, why it matters for legal practices, and how compliant IT services protect your firm. ... Read More
SOC 2 Compliance Made Simple: IT Controls Every Business Needs in 2026

SOC 2 Compliance Made Simple: IT Controls Every Business Needs in 2026

SOC 2 compliance has become a critical requirement for businesses handling customer data in 2026. This comprehensive guide breaks down the essential IT controls, security policies, and risk management frameworks needed to achieve and maintain SOC 2 certification. Whether you're a growing SaaS company, healthcare provider, or professional services firm in Orange County, understanding SOC 2 requirements protects your business from security risks while building customer trust. Learn how structured IT compliance services can streamline your audit preparation, implement necessary controls, and maintain ongoing compliance without disrupting daily operations. Discover practical steps to transform complex compliance requirements into manageable processes that strengthen your overall security posture. ... Read More
AI Policy Templates: Keep Your Teams Secure While Using ChatGPT

AI Policy Templates: Keep Your Teams Secure While Using ChatGPT

The crucial need for organizations to establish comprehensive AI governance frameworks and AI usage policies immediately, driven by the finding that most employees use AI tools without company guidelines. The sources emphasize that unmanaged AI adoption exposes businesses to serious threats, including the potential for data leakage of confidential information, intellectual property disputes, and costly compliance violations of regulations such as GDPR and HIPAA. To address these vulnerabilities, effective policies must define data classification guidelines, mandate the use of approved AI tools, and establish verification requirements to prevent flawed decision-making based on AI outputs. Furthermore, the imperative for secure AI requires continuous oversight from a governance committee, regular risk assessment of new tools, and mandatory training programs to ensure that employees understand responsible usage protocols. The overall goal is to strike a practical balance between leveraging AI's innovative capabilities and maintaining strict security controls, often achieved through external expertise in compliance management. ... Read More